

Restrict a project
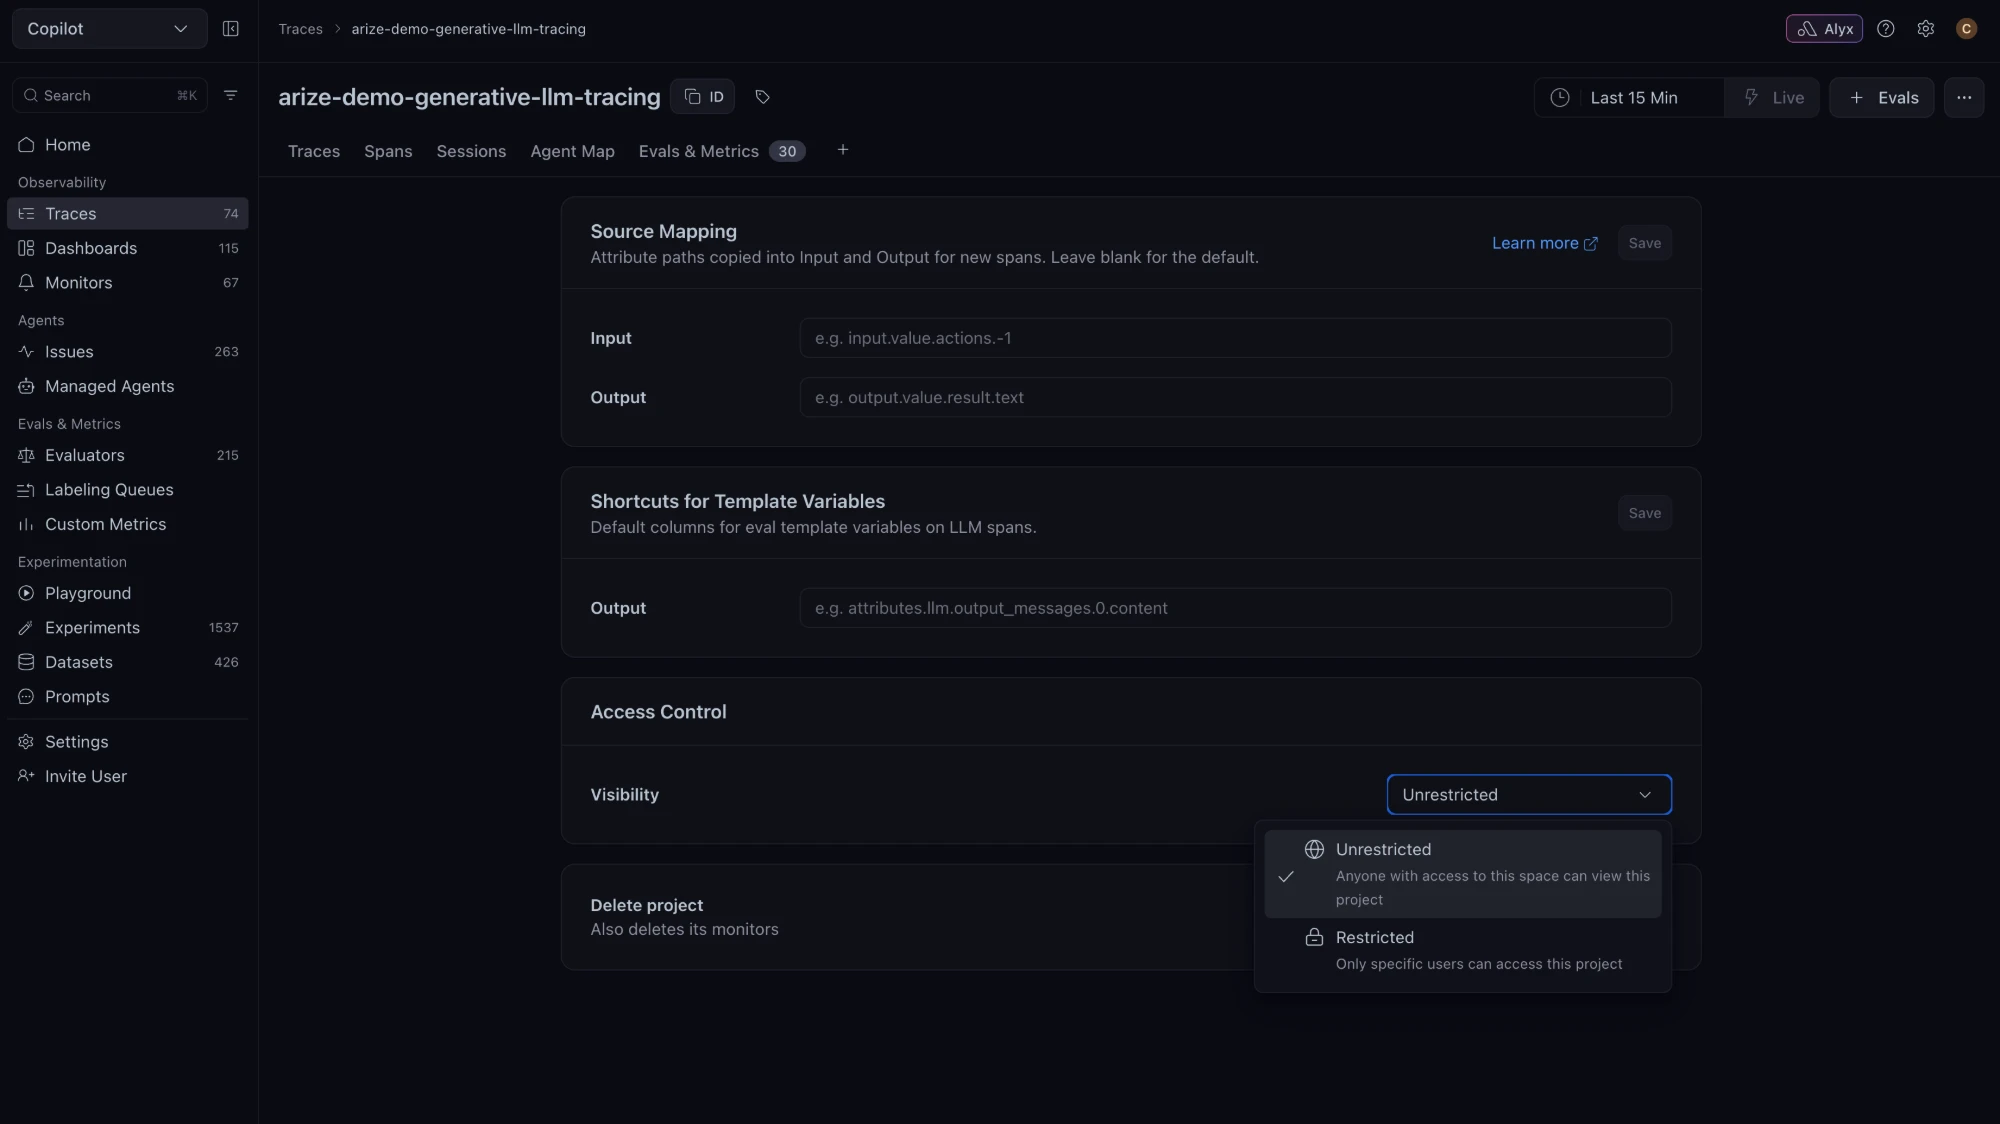
- Open the project, select the three-dot menu, and choose Config.
- Under Access Control, set Visibility to Restricted.
Restrict a dashboard
The dashboard’s access settings control who can see it. Everyone in this space follows each member’s space permissions. The restricted option limits the dashboard to the people you add.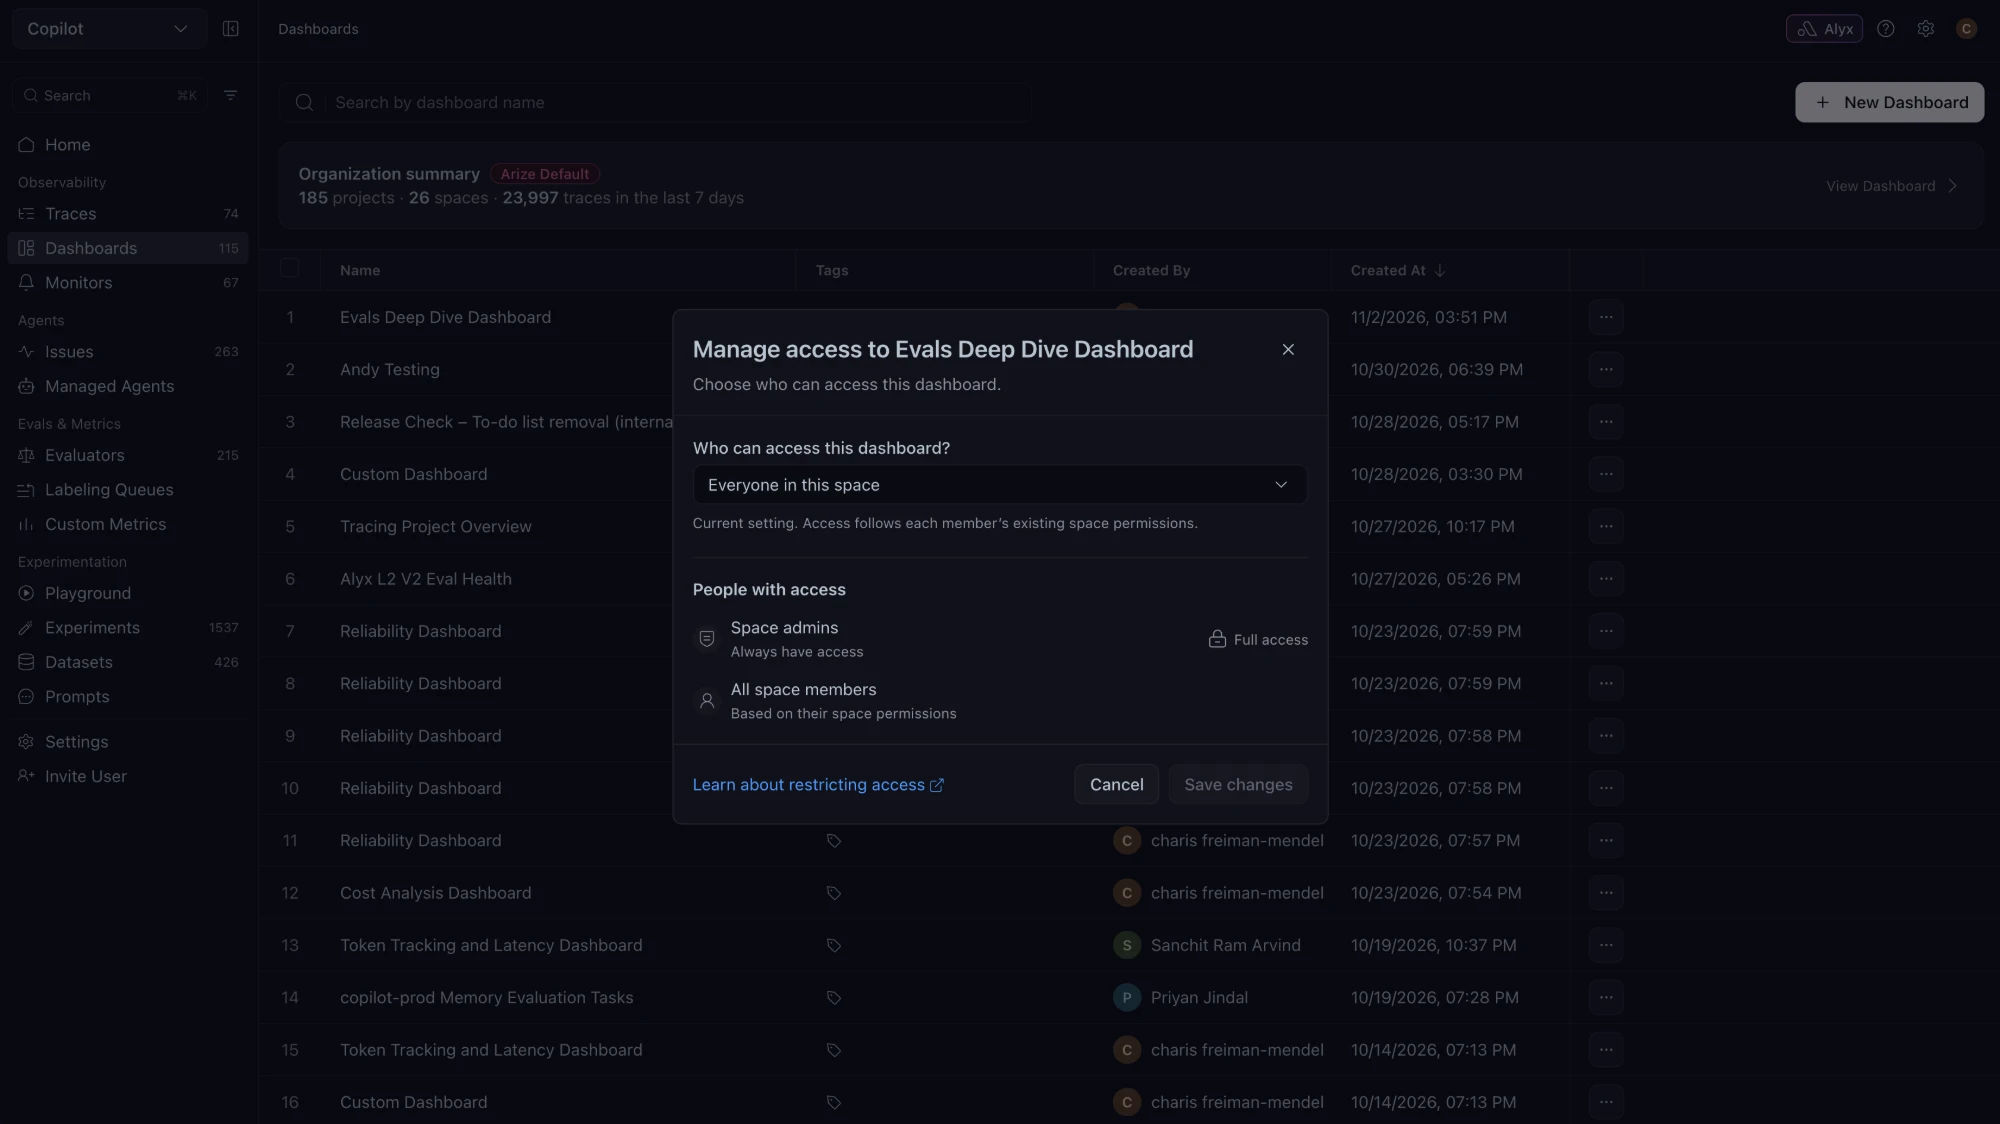
POST /v2/role-bindings accepts only SPACE and PROJECT, so a restricted dashboard is open only to space, organization, and account admins.
Restrict a prompt
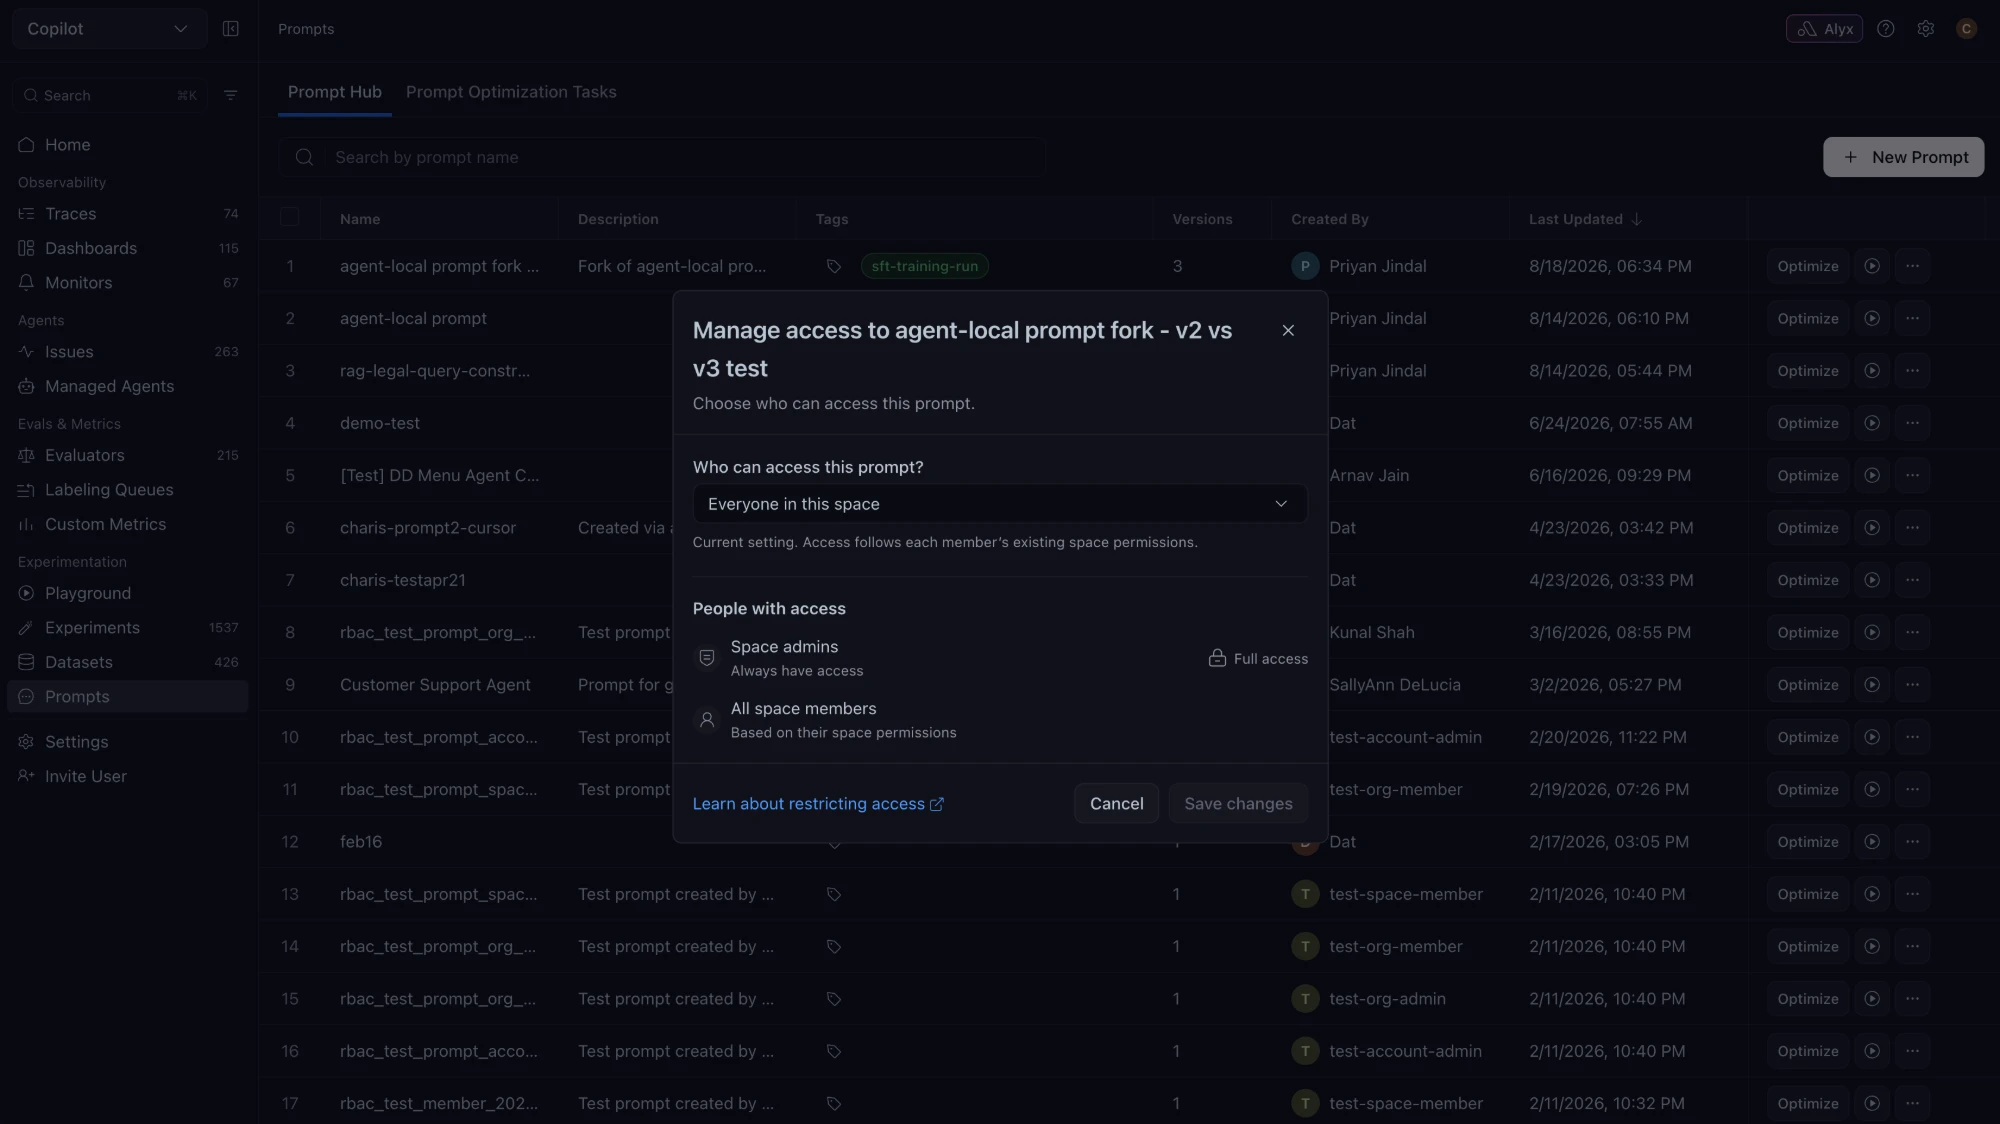
- In Prompt Hub, open the prompt’s row actions and select Manage Access.
- Choose the restricted option.
- Add the people who need access and save.
Project roles
Restricted projects use three managed roles.- Project Viewer reads spans and eval tasks.
- Project Editor also annotates spans and manages eval tasks.
- Project Admin has full access, including create and delete.
Use the REST API
POST /v2/resource-restrictions restricts a project or dashboard from its resource_id alone and DELETE /v2/resource-restrictions/{resource_id} removes the restriction. Both require space admin or the equivalent permissions, and restricting a resource that is already restricted has no effect. POST /v2/role-bindings grants a project role on a restricted project.
All endpoints are listed in the RBAC REST API.